
Unpacking Truth Behind Popular Myths Surrounding Ledger Crypto Wallets
Ledger Wallets Store Crypto Directly on the Device
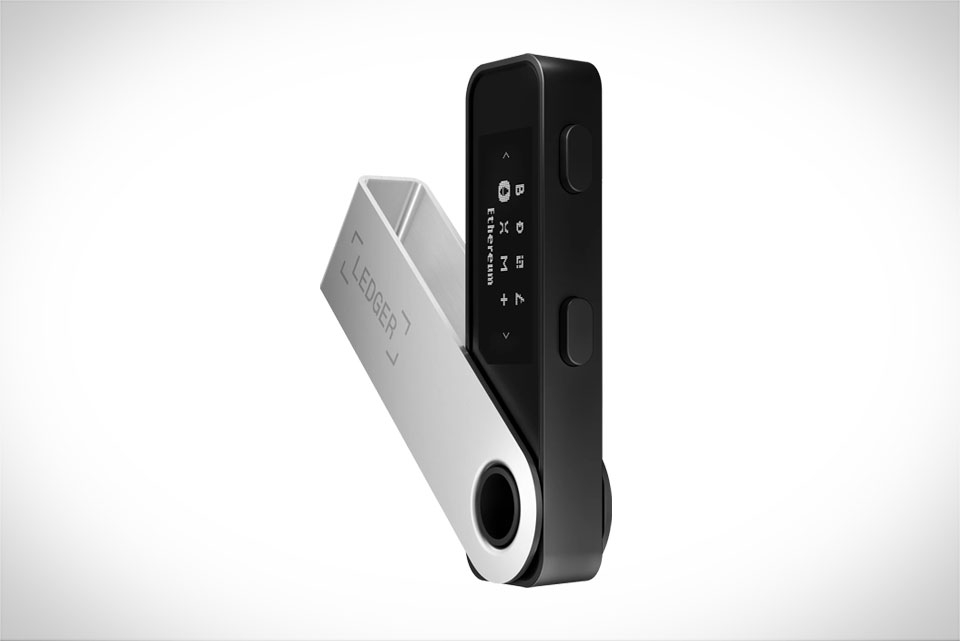
One of the most widespread myths is that your crypto holdings live on a Ledger hardware wallet like a USB drive storing files. But this isn’t how it works. Ledger devices (Nano S Plus, Nano X) generate and hold private keys offline—these are the only keys that sign transactions and access funds. The actual tokens (Bitcoin, Ethereum, etc.) reside on their respective blockchains, tied to public addresses linked to your private key. For example, if you own BTC in a Ledger wallet, your BTC stays on the Bitcoin blockchain, not the device. The Ledger’s role is to securely sign transactions when you press physical buttons, never exposing the private key to the internet.
Open-Source Code Makes Ledger Less Secure
Critics sometimes claim open-source code for Ledger’s firmware and apps is a weakness, since anyone can view or modify it. In reality, open-source is a major security strength. Ledger publishes code publicly on GitHub, letting independent researchers audit for vulnerabilities. A 2022 third-party audit by CertiK found and fixed minor code gaps before exploitation. Unlike closed-source wallets where the company controls all changes, open-source means no hidden backdoors. Top wallets like Trezor use the same model, and their security is widely trusted by the crypto community.
Lost Ledger Devices Mean Total Crypto Loss
A common fear is that losing your Ledger device—say, dropping it at a café—leads to permanent fund loss. This only applies if you skipped the critical step of backing up your recovery phrase. Ledger gives a 12, 18, or 24-word mnemonic phrase when setup; if your device is lost, import this phrase into a new Ledger (or any BIP-39 compatible wallet) to regain access. A Reddit user shared a story last year about losing their Nano S on a hike, then using their 24-word backup to recover 12 ETH and altcoins on a new Nano X in minutes. The only risk is if someone has both your lost device and backup, so storing the phrase offline (on metal) is key.
Ledger Can Remotely Steal or Access Your Funds
Another myth is that Ledger’s team can remotely hack your device to siphon funds. This is impossible due to Ledger’s Secure Element chip and offline design. The tamper-resistant Secure Element stores private keys, never connecting directly to the internet. Any transaction needs physical confirmation on the device—you must press buttons to approve transfers. Even if legally compelled, Ledger can’t trigger transactions or access your keys. A 2021 rumor about a “backdoor” was debunked by cybersecurity firm Trail of Bits, which found no hidden access points. This offline, user-controlled design makes hardware wallets far safer than always-connected hot wallets like exchanges.







