
Protecting Crypto Assets With Non-Extractable Key Logic
Core Principle: Private Keys Never Leave the Hardware Device
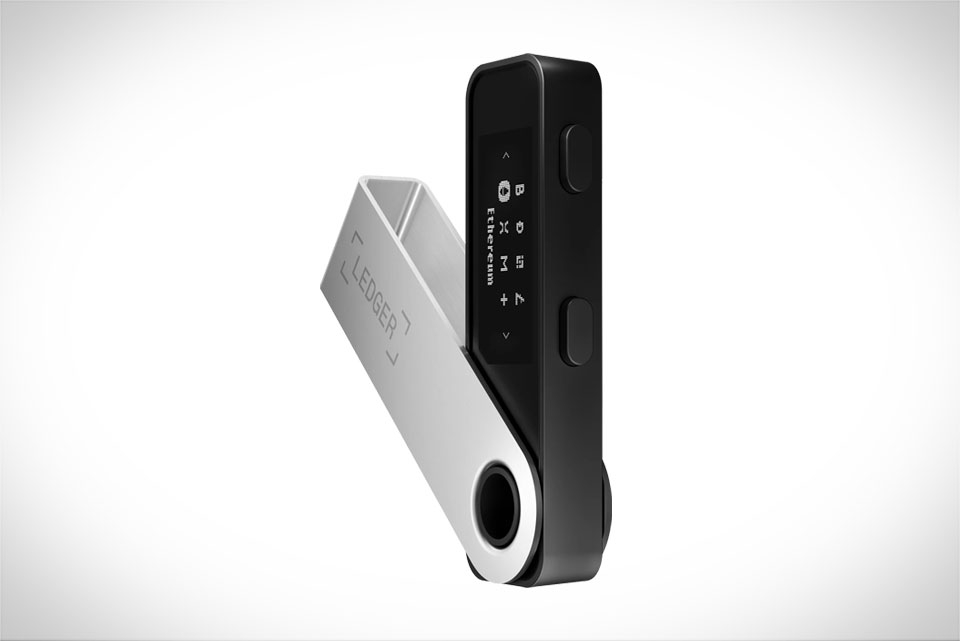
At the heart of Ledger’s security framework is a non-negotiable rule: private keys are generated, stored, and used exclusively inside the device’s secure element (SE), never transferred to external software or networks. Unlike hot wallets that store keys on browsers or cloud servers, Ledger’s hardware devices—such as the Nano S Plus or Nano X—create private keys only when the user initializes the wallet, and these keys are permanently locked within the SE chip. Even when you sign a transaction or approve an NFT transfer, the cryptographic operation happens entirely on the device; only the valid signature is sent back to your connected phone or computer, not the key itself. This isolation means no malicious software, phishing script, or hacked device can ever reach the private key, as it never leaves the secure hardware boundary.
The Hidden Dangers of Exposing Private Keys
Most crypto thefts stem from key exposure, a mistake many new users make when they export private keys from hot wallets or store them in plain text. Last year, a close friend of mine learned this the hard way: he stored his MetaMask private key in a notes app on his laptop, and when he clicked a fake “free NFT” link, a phishing script stole the key, draining his account of 3.2 ETH. If he’d used a Ledger, this theft would have been impossible—his private key never left the secure chip, so the phisher couldn’t access it even if he got control of his laptop. Even users who export keys from Ledger devices (a feature the official firmware discourages) risk exposing themselves; one crypto enthusiast I know accidentally sent his private key to a fake support email, losing 15 SOL in 2022. These cases show that key exposure is the single biggest threat to crypto holdings, and Ledger’s design directly eliminates this risk.
Hardware-Level Protections That Block Key Extraction
Ledger’s SE chip isn’t just a regular microcontroller—it’s a tamper-resistant component certified to CC EAL5+, the highest security level for consumer hardware. This means it’s designed to resist physical attacks like probing, voltage manipulation, or firmware tampering; if someone tries to physically open the chip to read its memory, the SE automatically wipes all sensitive data, including private keys. The firmware running on Ledger devices is also open-source, so independent security researchers worldwide can audit it for backdoors or vulnerabilities, ensuring no hidden code can steal keys. Even the device’s own operating system can’t access the private key directly—it only communicates with the SE for signature requests, making it impossible for malware or malicious apps to siphon off sensitive data. This layer of hardware security is far more reliable than software-based protections alone.
Real-World Validation & User Best Practices
Thousands of users have shared stories of avoiding theft thanks to Ledger’s key isolation rule. A well-known NFT collector I follow on Twitter uses Ledger to store over 200 rare NFTs, and he’s never faced a breach despite interacting with dozens of dApps weekly. His advice? Never export your private key from the hardware device, always update the firmware to the latest version, and only connect your Ledger to devices you trust (like your personal laptop, not public computers). Another user, a small crypto investor with a Ledger Nano X, told me that when his home laptop was infected with malware last year, the malware couldn’t access his private keys—all it saw was the Ledger’s standard signature output, not the sensitive data inside the SE. These real-world cases confirm that the simple rule of “private keys never leave the hardware” is the most effective defense against crypto theft today, and following basic best practices ensures long-term asset safety.







