
Simple checks to avoid counterfeit Ledger devices
Unboxing & Packaging First Checks
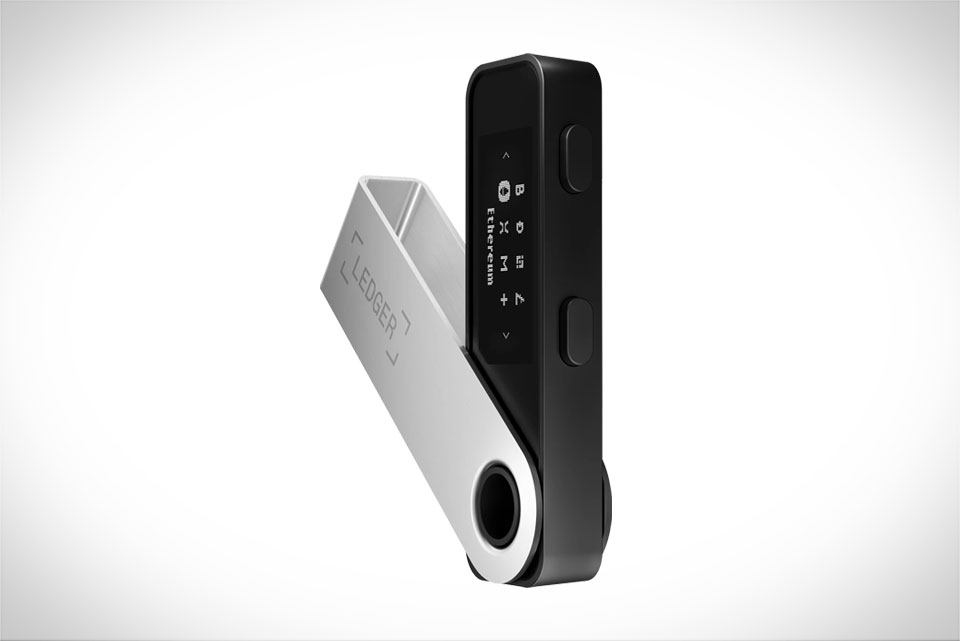
When your Ledger device arrives, start with the unboxing—this is your first line of defense against fakes. Official Ledger packaging has distinct, unique features: a tight, unbroken holographic seal on the outer box, matching batch numbers printed on both the box and inner tray, and crisp, non-faded branding. Last year, a Reddit user shared their experience buying a Ledger Nano S from a third-party seller; the package had a torn seal and no hologram, so they rejected it immediately. Never skip this step—any sign of tampering, even a small crease in the seal, could mean the device was opened, modified, or swapped. Also, confirm the device model matches what you ordered (Nano S Plus, Nano X, or Nano S) to avoid mislabeled fakes.
Device Physical & Serial Number Verification
Once you open the box, inspect the physical device closely. Official Ledger devices have no scratches, dents, or worn edges—fake ones often have scuffed USB ports or loose button presses. Next, cross-check the serial number: it should be printed on both the device’s back and the packaging box. Head to Ledger’s official serial number verification page (only accessible via ledger.com) and input the number. A friend of mine learned this the hard way: he bought a device from a local crypto meetup, the serial number on the device didn’t match the box, and the official page said it wasn’t registered, so he returned it. Fake devices rarely have matching serial numbers or valid registrations, as they’re mass-produced without Ledger’s tracking system.
Ledger Manager & Official App Validation
Next, validate the device via Ledger’s official software. Never download Ledger Manager or Ledger Live from third-party sites—these are often used to distribute malware. Only get the apps from ledger.com, the Apple App Store, or Google Play. When you connect the device to Ledger Live, the app should automatically recognize it as an official Ledger product. If it asks for a recovery phrase before you’ve set up the device, or shows an unrecognized model, disconnect it immediately. A crypto blogger tested a fake Ledger sold on an auction site; when they connected it to Ledger Live, the app flagged it as a counterfeit and refused to sync, so they avoided a potential theft.
Post-Setup Security Cross-Checks
After setting up your Ledger, do a final security check. When generating your recovery phrase, the device should display a random sequence of 12 or 24 words—never a pre-written list. Fake devices sometimes have pre-stored recovery phrases that scammers know. Also, update the firmware only through Ledger’s official firmware portal; if the update tool tries to install software from an unknown source, stop. Finally, test a small transaction first: send a tiny amount of crypto to your Ledger address. If the device doesn’t prompt you to confirm the transaction on its screen, it’s a fake—genuine Ledgers require physical confirmation on the device itself, no exceptions. This final step catches fakes that pass initial checks but lack core security features.







