
Practical steps to safeguard crypto with Ledger’s native tools
Offline Cold Storage: The Foundation of Ledger’s Security
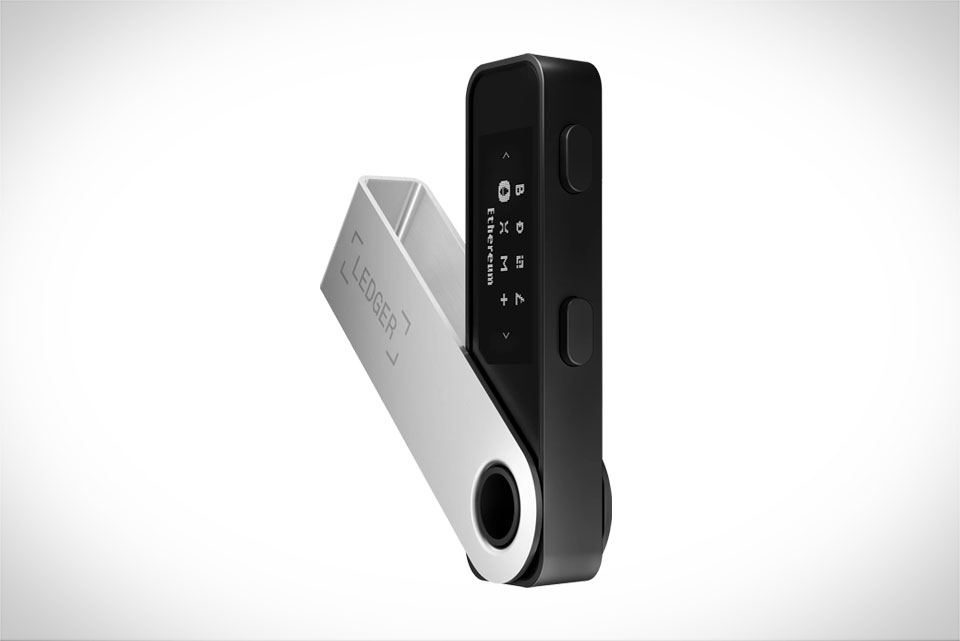
At the heart of Ledger’s security is its offline cold storage design, which keeps your private keys completely isolated from the internet. Unlike hot wallets that run on apps or browsers and are constantly exposed to online threats like keyloggers and phishing, Ledger devices store keys on the hardware itself, never transmitting them to any connected device unless you intentionally sign a transaction. For example, a friend of mine lost access to his MetaMask wallet after clicking a fake link that stole his seed phrase, but his Ledger Nano S remained untouched—even when he connected it to his work laptop, his private keys never left the hardware, so no malware could intercept them. This separation is non-negotiable for protecting large crypto holdings, as it eliminates the biggest risk of online theft.
Secure Element Chip: The Hidden Hardware Shield
Many users don’t realize that Ledger’s security isn’t just about being offline—it’s powered by a dedicated Secure Element (SE) chip, a certified component far more secure than regular microcontrollers. The SE acts as a vault within your Ledger device, isolated from the main processing unit, so even if someone gains access to the device’s firmware, they can’t extract or copy your private keys. When you initiate a transaction, the SE handles the cryptographic signing process, not the Ledger Live app on your phone or computer. A real-world example: last year, a security researcher tested an older Ledger model and found that hacking the main chip yielded no keys, because the SE blocked all unauthorized access attempts. Ledger’s SE is certified to CC EAL5+, a strict standard used in government and financial tools, making it nearly impenetrable to common hardware attacks.
Passphrase Protection: A Hidden Second Line of Defense
Beyond your 24-word recovery phrase and 6-digit PIN, Ledger offers a passphrase feature that adds an extra layer few users fully leverage. A passphrase is a custom word or phrase that creates a "hidden" wallet—if someone tries to access your Ledger without knowing this passphrase, they’ll only see an empty wallet, even if they have your PIN and recovery phrase. I learned this from a colleague who left his Ledger Nano X on a train; the finder tried random PINs three times (locking the device temporarily) and couldn’t access his $20k in Ethereum, because no one knew his passphrase. It’s critical to remember that passphrases are not stored by Ledger, so you must write yours down separately from your recovery phrase—never keep them in the same place, or this extra layer becomes useless.
Firmware Updates and Phishing Resistance: Stay Proactive
Even with built-in security, Ledger users must stay proactive with firmware updates and phishing awareness. Ledger regularly releases firmware patches to fix newly discovered vulnerabilities; skipping these updates can leave your device exposed. For instance, in 2022, Ledger issued an urgent update to block a flaw that allowed attackers to intercept transaction data; users who updated immediately avoided potential theft, while those who delayed faced higher risks. You can check for updates directly in the Ledger Live desktop app, which prompts you when a new version is available—never use unofficial tools to update, as these could be malicious. Additionally, phishing is constant: Ledger will never ask for your recovery phrase, passphrase, or PIN via email, text, or social media. A common trap is fake Ledger Live apps that steal credentials; always download only from the official Ledger website or trusted app stores. This combination ensures you don’t fall for avoidable gaps that could compromise your assets.







