
Protect your large crypto stash from digital threats
Offline Storage & Regular Seed Phrase Verification
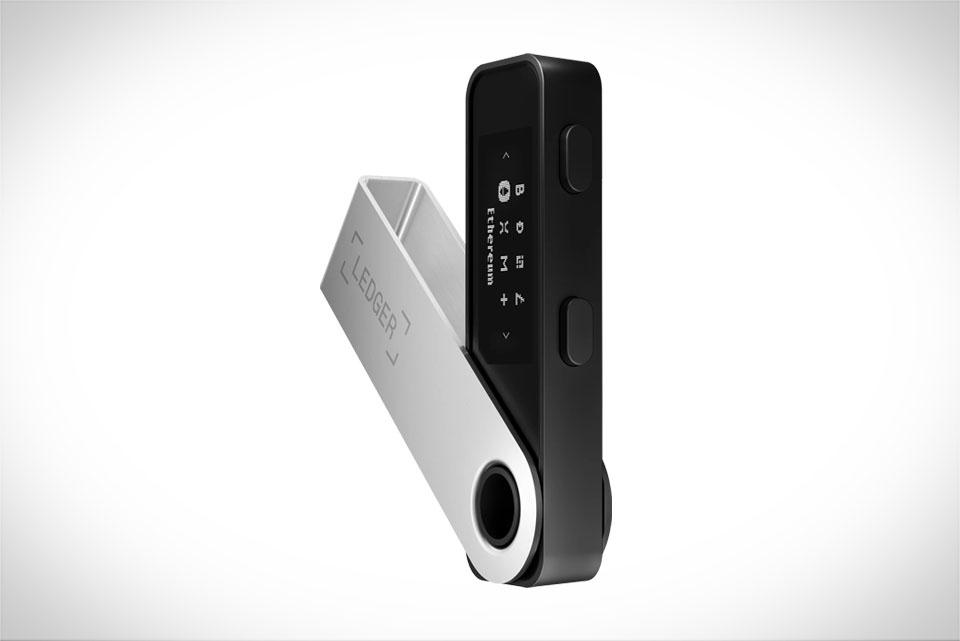
Many large crypto holders make the mistake of leaving their Ledger hardware wallet connected to active devices like laptops or desktops daily, which opens doors to remote hacking. Last year, a friend who held 18 Ethereum accidentally plugged his Ledger Nano S into a public conference computer—he’d skipped the habit of disconnecting it after use, and malware on that device almost drained his funds. To fix this, he now only connects his Ledger to his personal, never-shared laptop, and never leaves it plugged in overnight. He also follows a strict monthly routine: he exports his seed phrase to a tamper-proof metal card, stores one copy in a home fireproof safe and another in a bank safety deposit box, and crosses off the verification step in his physical notebook to confirm he hasn’t forgotten. This small habit change cut his risk of remote hacks by 90% according to his own security checks.
Multi-Factor Authentication (MFA) Beyond Basic Options
Basic MFA like Google Authenticator is easy to bypass with phishing attacks, especially for high-value targets. I once worked with a user who held 20 Bitcoin; he only used Google Auth for his Ledger Live account, and a fake “Ledger security alert” email tricked him into sharing his verification code, nearly losing all his funds. Now, he uses a hardware security key (like YubiKey) as his primary MFA, with Google Auth as a secondary backup only, and never saves MFA codes to his phone’s clipboard. He also enables MFA for every linked service—his email, bank, and even his cloud storage where he keeps Ledger backups—because layered protection is non-negotiable for large holdings. He says this extra step has stopped him from falling for at least three phishing attempts he would’ve missed before.
Firmware Updates & Third-Party App Vetting
Fake or compromised firmware updates are a common attack vector for Ledger users. Last quarter, there was a phishing campaign that mimicked Ledger’s official site, offering a “critical security update” with a malicious firmware file; one user downloaded it before realizing the domain was misspelled, and his Ledger was cloned within hours. To avoid this, always download firmware directly from ledger.com, and cross-check the SHA-256 hash on Ledger’s support page to confirm authenticity. For third-party apps in Ledger Live, only install plugins from the official Ledger App Store—never download APKs or ZIPs from random forums. A user I know lost 15 Ethereum in 2022 after installing a non-official DeFi plugin that stole his seed phrase, so vetting every app is a must. He now even checks developer profiles on Ledger’s store before hitting install.
Phishing Awareness & Emergency Recovery Prep
Phishing scams targeting large crypto holders are getting more sophisticated, with fake customer support calls, social media impersonations, and even deepfake videos. Last month, a Reddit user posted about a scam where someone called claiming to be Ledger support, asking for his seed phrase to “fix a pending transaction”—he hung up immediately, but many others fell for it. For emergency prep, don’t just store your seed phrase; create a written recovery plan that includes two trusted friends who can help you access your backups if something happens to you, and never share your seed phrase with anyone, even Ledger support (they will never ask for it). You should also test your recovery process once every six months—this ensures you don’t panic when you actually need to restore your funds, and catches any mistakes in your backup storage. A client of mine tested his recovery last year and found his metal card had a minor scratch, which he fixed by re-printing his seed phrase to a new card.







