
Step-by-step ways to confirm your Ledger is unaltered
1. Unboxing: Check Physical & Packaging Integrity
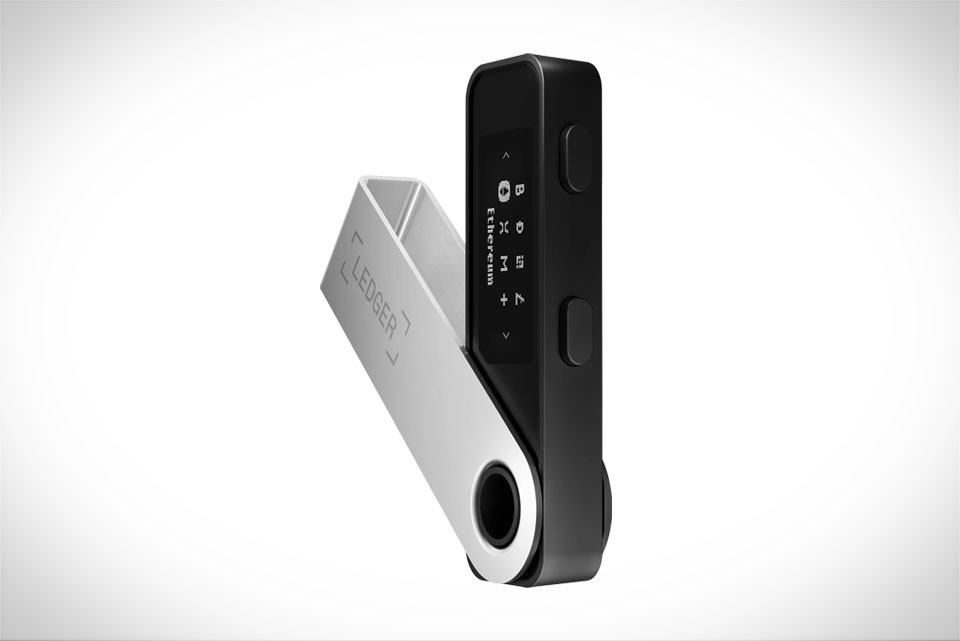
When your Ledger device arrives, the first line of defense is the unboxing process—never skip this, as tampering can happen at shipping. Ledger’s official packaging uses tamper-evident holographic seals; these should be fully intact, with no tears, scratches, or misalignments when you open the box. A crypto user in a Reddit community recently spotted their Ledger Nano X’s seal partially peeled before opening; they contacted Ledger support and got a replacement, avoiding potential fraud. Also, cross-check the device’s serial number on the back with the one on the original packaging. If the numbers don’t match, the device is likely swapped—stop right there. Avoid second-hand Ledger devices unless you verify every detail with Ledger’s team, as used units carry higher tampering risks.
2. Initial Setup: Validate Serial Number & Official Pairing
After unboxing, don’t connect the Ledger to your computer or phone right away. First, head to Ledger’s official website and use their serial number verification tool—input the number from your device’s back to confirm it’s genuine, not a counterfeit. During setup, when you’re prompted to write your recovery phrase, never skip confirming each word as the device asks; this built-in step ensures the device generates a legitimate seed. A friend of mine tried setting up a Ledger and the device asked for an extra code beyond the standard 12/24-word phrase, which isn’t part of official guides. He stopped and contacted Ledger, avoiding a fake setup that would’ve stolen his seed. If the setup asks for unlisted extra steps, it’s a red flag.
3. Firmware & App Updates: Stick to Official Channels Only
Never download Ledger firmware or apps from third-party sites, forums, or peer-to-peer platforms—these are common sources of tampered software. Ledger only provides updates via Ledger Live (desktop or mobile), signed with its official digital certificate. When updating firmware, ensure you’re using the latest Ledger Live version and the update shows a successful signature check. A well-known case involved a user who downloaded modified Ledger firmware from a Reddit thread, which had a backdoor to steal private keys. Within 24 hours of installing, their crypto assets were drained. Always check Ledger’s official blog for firmware release notes to confirm no suspicious changes, and never trust “beta” versions from unofficial sources.
4. Transaction Confirmation: Cross-Check Offline Details
Ledger’s core strength as a cold wallet is offline transaction confirmation—critical for avoiding tampering. Whenever you initiate a send, receive, or swap, the Ledger screen shows key details: recipient wallet address, crypto amount, and network fee. You must compare these exactly to what’s on Ledger Live. If there’s a mismatch—like the device showing a different address than the app—stop immediately, as this signals a man-in-the-middle attack or compromised device. Last month, a user reported their computer displayed a stablecoin transfer address, but their Ledger Nano S showed a completely different one. They didn’t confirm and contacted Ledger, which traced the issue to a malicious script on their computer intercepting details. Always double-check, even if you’re in a hurry to complete a transfer.







