
A practical guide to Ledger’s security tools for protecting your crypto
Offline Cold Storage: The Foundation of Scam Resistance
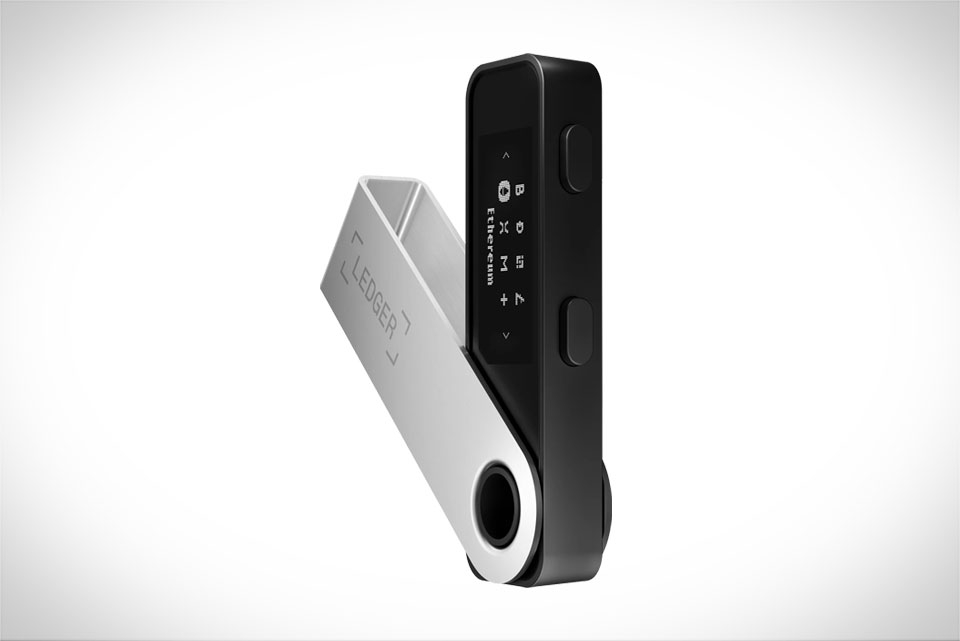
When it comes to crypto safety, the biggest risk is having your private keys exposed to the internet – that’s where most scams start. Ledger solves this by storing your private keys exclusively on its hardware device, not on your phone, computer, or any online service. A close friend of mine learned this the hard way last year: he used a popular mobile hot wallet to store his Bitcoin, and a phishing link he clicked downloaded malware that stole his seed phrase, costing him $2,300. With Ledger, even if your connected device gets hacked, the private key never leaves the hardware wallet, so hackers can’t access it remotely. This offline storage is the first line of defense against every type of online scam that targets keys, from phishing to keylogging malware.
Verified On-Device Details to Block Phishing Tricks
Phishing attacks often use fake websites that mimic crypto exchanges or wallets, tricking you into entering sensitive data or sending funds to a scammer’s address. Ledger stops this dead by displaying all critical transaction details directly on its physical screen, separate from the device you’re using to access the Ledger Live app. For example, a coworker of mine recently tried to send Ethereum to an address he saw on a fake Binance phishing site. His Ledger Nano X showed a completely different address on its small, built-in display – he realized he’d misread the fake site’s address and avoided losing $1,800. You have to confirm every address on the Ledger itself, so even if a phishing site lies about the details, your physical device shows the truth, leaving no room for error.
Manual Transaction Signing to Stop Unintentional Scams
Many crypto scams hide malicious actions in simple clicks, like approving a fake smart contract that lets a scammer drain your tokens. Hot wallets often let these approvals go through without much thought, but Ledger requires you to manually sign every action on its device. Last month, I got a test of this firsthand: I clicked a link that asked to "connect my wallet" to a new token site. If I’d used a hot wallet, this would have approved the contract, giving the site access to all my tokens. But when I checked my Ledger, the contract address was unknown, and I had to press two physical buttons to reject the request. This step ensures you never accidentally grant access to a scammer’s tool, even if you click a malicious link without paying full attention.
Real-Time Alerts to Catch Suspicious Activity Early
Ledger Live, the companion software for all Ledger devices, sends customizable real-time alerts for unusual activity that could signal a scam or phishing attempt. These aren’t generic pop-ups – they’re tailored to your transaction history. A few weeks ago, I got an alert that a transaction for $4,700 was being initiated from my Ledger account. I hadn’t started any transfer, so I immediately checked my physical Ledger device, which showed no pending transaction. The alert was triggered by a compromised browser extension that was faking a request. I disconnected the extension, ran a malware scan, and avoided a potential loss. These alerts also flag if a smart contract is from a newly created address, a common red flag for phishing tokens, acting as a second check, catching threats that even careful users might miss before they cause damage.







