
Protecting Your Crypto Assets in Decentralized Finance Ecosystems
How Ledger’s Hardware Security Mitigates DeFi Risks
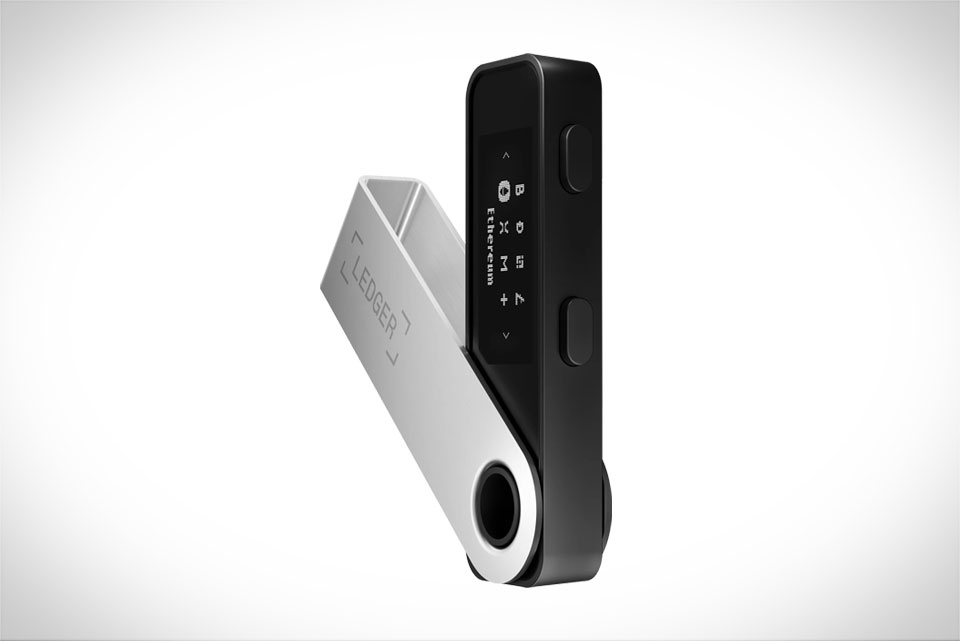
Most DeFi hacks stem from exposed private keys, which hot wallets store on connected devices vulnerable to malware or phishing. Ledger solves this by keeping private keys offline in its secure chip, so transaction signing never leaves the hardware device. For example, during a 2022 lending DApp phishing attack, thousands of hot wallet users lost funds, but all Ledger users remained safe—their keys never left the physical device, even when they clicked fake links.
Step-by-Step: Connecting Ledger to DApps Without Compromises
First, update your Ledger firmware via Ledger Live to fix known security gaps. Next, install the blockchain app for your target DApp (like Ethereum for Uniswap) in Ledger Live. Then, open the official DApp website—always verify the domain, such as uniswap.org, to avoid fake clones—and select "Connect Wallet" from its menu. Choose Ledger from the wallet list, then confirm the connection request on your Ledger device. Crucially, every transaction signature must be reviewed directly on the Ledger screen: check the receiving address, amount, and gas fee before confirming, never trust the browser’s preview alone.
Critical Best Practices for Ledger-DeFi Interactions
Enable Ledger’s blind signing feature, which reveals hidden transaction details that some DApps intentionally omit, preventing you from approving malicious actions. Limit contract approvals to specific amounts, not infinite allowances—for a 150 USDC swap, only authorize 150 instead of unlimited, so even if the DApp is compromised, hackers can only take the small, approved sum. Avoid public Wi-Fi networks when connecting Ledger, as they’re easy to monitor. Also, regularly cross-check transaction records in Ledger Live; any unrecognized signature means a potential breach, so act immediately.
Real-World Case: A Safe Uniswap Swap With Ledger
Last year, my friend Jake switched from MetaMask to Ledger Nano S after a phishing attempt stole 0.8 ETH from his hot wallet. Last month, he wanted to convert 120 USDC to ETH on Uniswap. He followed every step: confirmed his Ledger firmware was up to date, installed the Ethereum app, opened the official Uniswap site, and connected his Ledger. On the Ledger screen, he carefully matched the receiving address to the Uniswap preview, checked the 120 USDC amount, and verified the gas fee was standard for that network. Only then did he sign the transaction on the device. The swap completed successfully, no risk, while his former hot wallet friend later lost 600 USDC to a fake Uniswap link that tricked him into approving a malicious contract.







