
Protecting your digital assets for years to come
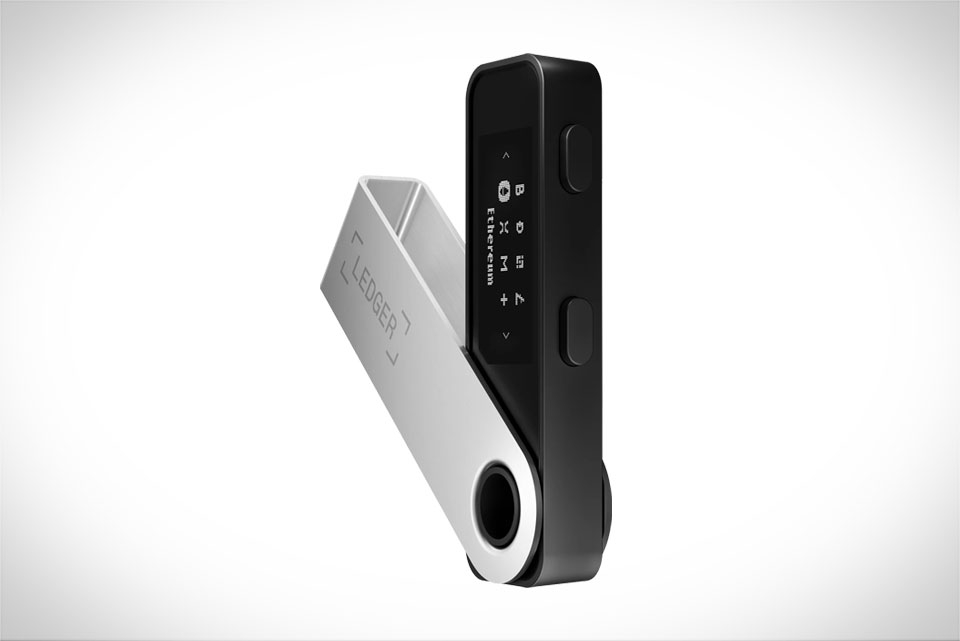
When it comes to storing crypto assets for the long term, Ledger hardware wallets are one of the most reliable tools, but only if you follow specific best practices. Many users assume that owning a Ledger is enough, but gaps in security habits can lead to irreversible losses. For example, a colleague of mine lost $15,000 worth of Ethereum last year because he stored his 24-word recovery phrase in a cloud note that was hacked – this is exactly why consistent, careful steps matter for long-term storage.
Secure Your Recovery Phrase Properly
Your Ledger’s recovery phrase is the master key to all your funds, not the device itself. If your Ledger is lost, stolen, or broken, the only way to restore access is with this phrase. Never store it digitally: avoid notes in your phone, cloud storage, or email, as these are vulnerable to hacks and leaks. Instead, use a physical steel wallet (like Ledger’s own Steel or Cryptosteel) that’s fireproof, waterproof, and corrosion-resistant. For added security, consider splitting the phrase using Shamir Backup if your Ledger model supports it – this splits the 24 words into separate groups, so no single person or thief can access your funds even if they find one part. I recommend testing your backup once a year by entering the phrase on a spare Ledger or a test device to confirm it works, which prevents last-minute panic if the backup is unreadable.
Keep Firmware and Apps Updated
Ledger regularly releases firmware and Ledger Live app updates to fix security vulnerabilities, add support for new cryptocurrencies, and improve performance. Skipping these updates leaves your device open to known exploits. Last year, a firmware update patched a flaw that allowed attackers to intercept transaction data during setup; users who delayed the update were at higher risk of phishing attempts. Always install updates only through the official Ledger Live app or the verified Ledger website. Never click on pop-up links in emails or social media that claim to offer Ledger updates – these are almost always phishing scams. When updating, double-check that the device screen prompts you to confirm the update, as this ensures the process is tamper-proof.
Avoid Unofficial Channels for Transactions and Updates
Scammers target Ledger users with fake websites, phishing links, and third-party tools that steal recovery phrases or funds. Last month, I almost fell for a fake Ledger Live site with the domain ledger-live.co instead of the official ledger.com – the difference was subtle, and I only caught it because I always check the URL before entering sensitive info. When sending assets, never trust the receiving address displayed on your computer screen; malware can alter the address in real time. Instead, always cross-verify the address on your Ledger device’s physical screen before confirming the transaction. Don’t use third-party plugins or tools that claim to “enhance” Ledger features – these are designed to steal your keys. Stick strictly to Ledger’s official tools and verified, regulated exchanges for all transactions.
Regularly Verify Asset Accessibility and Backup Health
Long-term storage isn’t a set-it-and-forget-it task. Every 6 to 12 months, take time to confirm your assets are accessible and your backup is in good shape. A user in a popular crypto forum shared his story last year: he’d stored his Ledger in a safe for 4 years, but when he tried to access his funds after a family emergency, he found the device’s battery had corroded, and he had to rely on his backup. If he’d tested his backup earlier, he would have known the device was at risk. To avoid this, check that your Ledger is stored in a cool, dry place away from extreme temperatures. Test your recovery phrase by restoring it to a new Ledger (never use your main device for this test) to ensure no words were miswritten. Also, confirm your steel backup isn’t damaged, and that you have a secondary backup in a separate, secure location – this adds an extra layer of protection if one backup is lost or destroyed.







